

SEON expands fraud signals to spot AI-made identities
Tue, 29th Sep 2026 (Today)
SEON has expanded its Signal Intelligence data set for fraud prevention and anti-money laundering, increasing its proprietary signal count from more than 900 to more than 1,100.
The added coverage includes address intelligence, session behaviour, and phone and carrier data, along with broader digital footprint and device signals. The changes are intended to help risk teams identify inconsistencies in customer identities and detect links between accounts without adding extra steps for users.
The expansion comes as fraud specialists face a rise in synthetic identities and AI-generated deception. SEON cited industry concerns that generative AI tools now allow criminals to create convincing profiles, deepfakes, and device histories far more quickly than before.
For investigators, the challenge is that individual checks can appear normal when viewed alone. An email may validate correctly, a device may seem unremarkable, and an address may pass verification, while signs of fraud emerge only when those data points are assessed together.
The broader signal set is designed to strengthen three areas of analysis: an identity's history, the infrastructure connected to it, and behaviour during live sessions. The data can then be fed into rules, analyst reviews, and AI-based investigations within SEON's platform.
Identity history
One part of the expansion focuses on whether an email address or phone number shows evidence of longer-term use. Digital footprint checks now extend across a wider range of online services, including AI developer platforms, job boards, real estate sites, and dating apps.
Phone intelligence has also been expanded to include SIM-swap and number porting history. These signals can help risk teams judge whether an identity appears established over time or was assembled for a specific transaction or account opening.
Shared infrastructure
Another area focuses on infrastructure that may be reused across fraud networks. SEON's address intelligence tools standardise and verify address data across more than 240 countries, assigning identifiers to exact addresses and buildings so investigators can spot patterns hidden by formatting differences or unit-number variations.
Device intelligence has also been broadened. The new signals can indicate AI-agent activity, compromised iOS devices, Android eSIM mismatches, and differences between network country data and visible IP locations where a VPN may be masking traffic.
These checks are intended to expose situations where multiple accounts are linked by common operational infrastructure rather than obvious identity details. That can be important in organised fraud cases, where criminals spread activity across many apparently separate users.
Live behaviour
SEON has also expanded session monitoring beyond onboarding to login, account recovery, checkout, and payment flows. Teams can use this to identify automation, remote access, off-screen activity, and active calls while a session is taking place.
This approach is intended to give investigators a chance to intervene before suspicious behaviour develops into account takeover or payment fraud. It also shifts some analysis from static sign-up checks to behaviour observed throughout the customer journey.
Every signal in the update can be used in alerts, rules, customer reviews, and network investigations. The data is also available through SEON's Model Context Protocol server for investigators using external AI tools.
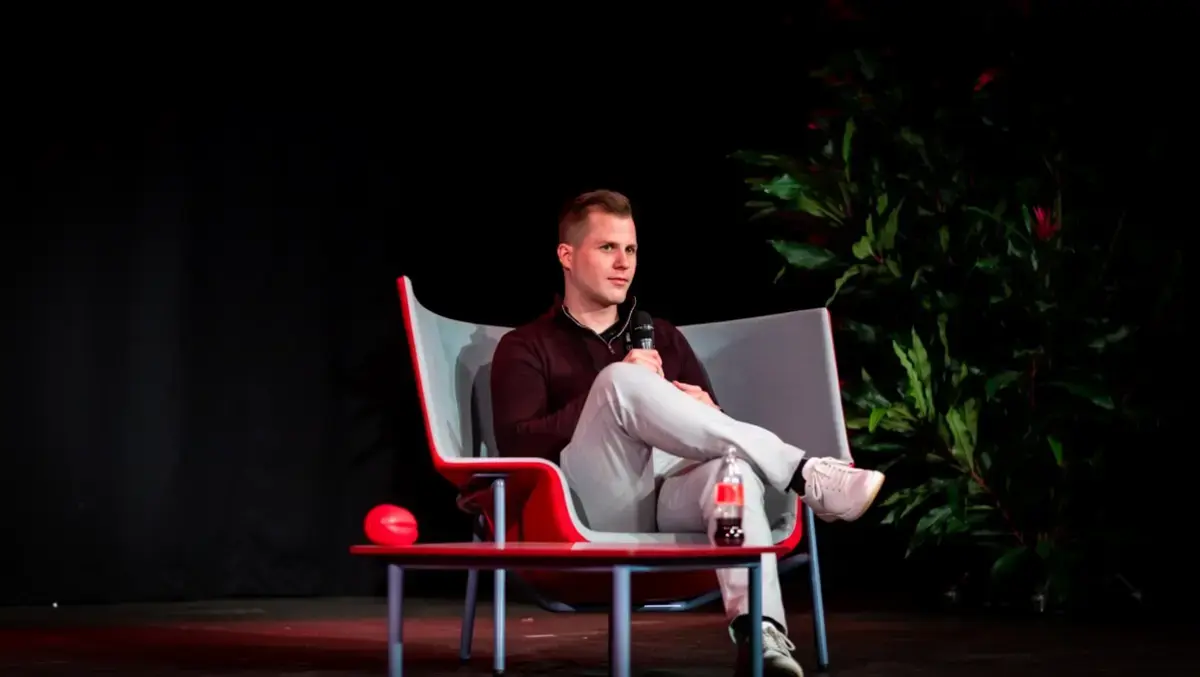
Tamas Kadar outlined the company's view of why fraud detection is becoming harder. "AI has made a believable identity cheap to produce. What fraudsters cannot easily do at scale is build a consistent history for every account without reusing infrastructure," said Tamas Kadar, Chief Executive Officer and Co-Founder, SEON.
"That is where our signal foundation makes the difference. The more dimensions a fraud team can check simultaneously, the harder it is to hide an identity that does not add up," Kadar said.
SEON has also introduced a research series called Hidden Risk Files, which presents short case studies from its fraud consultants. The series is intended to show how particular signals can uncover patterns that broader checks may miss.
The first example focuses on a device attribute linked to screen brightness, which connected thousands of accounts in a fraud ring operating across real Android hardware.