

Irish SMEs lose 34 hours on average after cyberattack
Tue, 22nd Sep 2026 (Today)
Irish small and medium-sized businesses hit by a successful cyberattack lost an average of 34 hours of operations, according to new research from Hiscox. The findings are based on a survey of 300 Irish businesses with fewer than 250 employees.
The study found that the effects went beyond immediate disruption to systems and services. Among businesses that had experienced a successful attack in the previous 12 months, 36% said they lost business opportunities or partnerships, 34% delayed growth, expansion or new business initiatives, and 34% reported an effect on financial performance, valuation or credit rating.
Another 32% said an attack had delayed the adoption of artificial intelligence or other new technologies. The figures suggest cyber incidents are shaping commercial decisions as well as day-to-day operations at smaller Irish companies.
Wakefield Research conducted the survey among cybersecurity decision-makers in Irish businesses. The wider international report covered 6,800 respondents across several markets, but the Irish findings point to a distinct strain on smaller firms with limited resources.
“Cybersecurity is no longer simply a technology issue. For an SME, losing almost a full working week to disruption can mean delayed orders, missed opportunities, pressure on cash flow and valuable management time being diverted away from customers and growth.
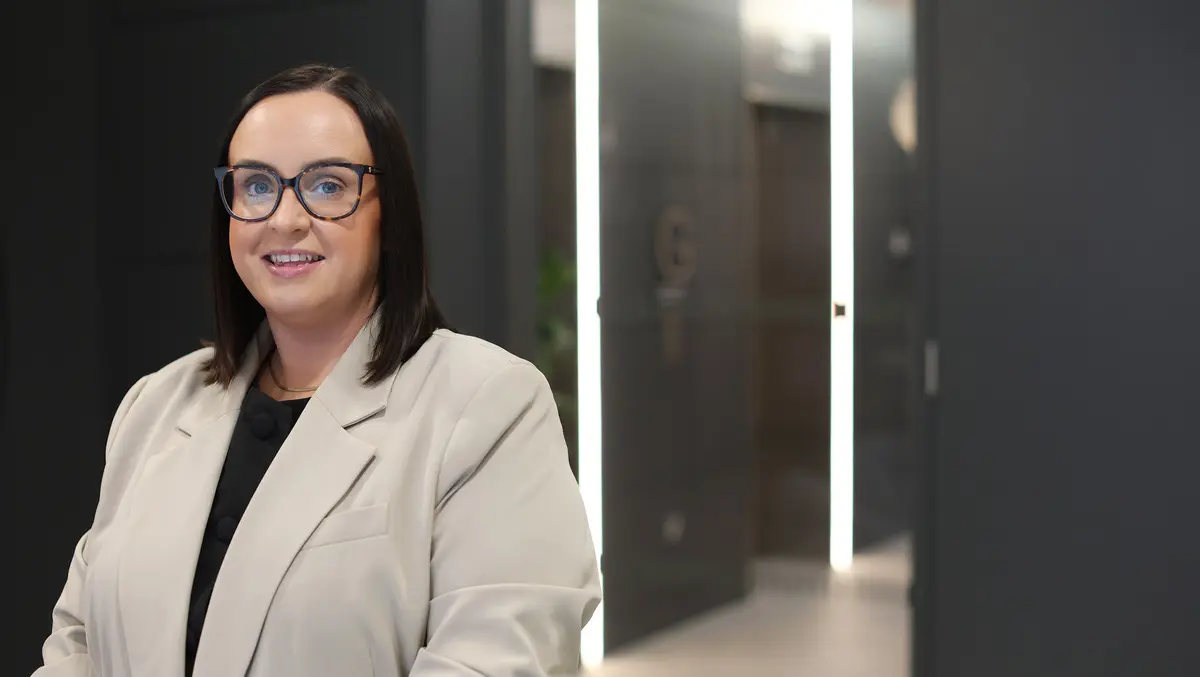
“Smaller businesses often face many of the same sophisticated threats as larger organisations, but without the same depth of in-house cybersecurity, fraud-prevention or compliance resources. That makes preparation, clear responsibilities and access to the right support particularly important,” said Ciara Weldon, senior development underwriter at Hiscox Ireland.
Boardroom focus
The research also indicates that cyber risk is moving further up the management agenda. More than one in three businesses affected by a successful attack, or 36%, said leadership compensation or performance measures were linked to cybersecurity goals.
A further 34% said they had increased their use of external cybersecurity expertise, while 33% said they had created or updated cyber crisis-response plans. These responses point to a growing willingness among smaller companies to treat cyber risk as a governance issue rather than only a technical one.
“Business leaders do not need to become cybersecurity specialists, but they do need to understand the potential consequences of an incident and ensure clear responsibilities, appropriate controls and tested response arrangements are in place.
“For SMEs, responsibility for cybersecurity may be shared across leadership, operations, IT and trusted external advisers, which makes clarity around roles and response planning particularly important,” Weldon said.
Broader risks
Across the full Irish sample, 48% ranked reputational damage or loss of customer trust among their greatest business risks. Operational downtime or business interruption and supply-chain or third-party disruption were each cited by 47%, while 46% included regulatory compliance among their leading concerns.
These concerns reflect how heavily smaller companies now depend on digital tools, cloud systems, payment providers and outside technology partners. A cyber incident affecting a supplier can interrupt trading even if a company's own systems remain untouched.
That dependency means the consequences of an attack can spread to customer relationships, partner confidence and investment decisions. For companies already operating with lean teams and tight budgets, prolonged disruption can quickly become a wider business problem.
“The wider impact of an attack can continue long after systems are restored. A cyber incident can affect financial performance, business relationships, customer confidence and the ability to move forward with new investment or expansion.
“That is why cyber resilience needs to be treated as a core business discipline rather than an issue owned solely by the IT department,” Weldon said.
Response measures
The report suggests many Irish businesses are increasing spending and planning around cyber risk. Some 68% said they were updating cybersecurity training for employees, 57% were investing in cybersecurity software, and 55% were hiring additional staff to manage cybersecurity.
It also found that 67% of Irish businesses currently have cyber insurance. That level of take-up suggests firms are seeking a mix of financial protection and access to outside help when incidents occur.
For insurers and advisers, the data offers a snapshot of how cyber risk is being absorbed into routine management decisions at smaller companies. It also shows that attacks are no longer viewed only as an IT outage, but as events that can affect trading, strategy and reputational standing.
“The businesses making the greatest progress are those that treat cyber resilience as a combination of people, technology and process. For SMEs, that does not necessarily mean complex governance structures or major technology investment. Clear responsibilities, practical employee guidance, proportionate controls and a tested response plan can make a meaningful difference.
“Preparation is also about more than trying to prevent every possible attack. Businesses need to know how they will respond, who they will contact and how they will restore operations quickly.
“Cyber insurance should be considered as part of a wider resilience strategy. Alongside financial protection, its value can include rapid access to forensic specialists, legal advisers, crisis communications support and recovery expertise when time is critical,” Weldon said.